On this page
Self-Hosting with Headscale
Aircast reaches your device over a tailnet: a private WireGuard mesh coordinated by a control server. By default that's Tailscale's hosted coordination service. If you'd rather own the whole path, point the device at your own Headscale server instead. No Tailscale account and no third-party coordinator, just your control plane and your devices.
Before you start
- A small always-on host with a public IP or DNS name for Headscale (a $5 VPS is plenty, since it carries control traffic, not video).
- A domain with HTTPS for the control server. Headscale clients require TLS; terminate it with Caddy, a reverse proxy, or Headscale's built-in ACME.
- An Aircast device already flashed and reachable on your LAN, see First flight. Or set Headscale while you flash the card, see step 5.
Throughout this guide, replace https://headscale.example.com with your own control server URL.
Set it up
Deploy Headscale
Headscale reads its config at startup, so create the data and config directories first. Grab the example config and set server_url to your public URL:
mkdir -p ./config ./data
curl -fsSL https://raw.githubusercontent.com/juanfont/headscale/main/config-example.yaml \
  -o ./config/config.yaml
# edit ./config/config.yaml → set: server_url: https://headscale.example.com
Then start the container, mounting both directories:
docker run -d --name headscale \
  -v ./config:/etc/headscale \
  -v ./data:/var/lib/headscale \
  -p 8080:8080 \
  headscale/headscale:stable \
  serve
Front it with HTTPS so it's reachable at https://headscale.example.com, Headscale clients require TLS. Verify it's up:
curl -fsS https://headscale.example.com/healthSee the Headscale documentation for the full config reference and reverse-proxy examples.
Connect the admin panel
Everything from here on happens in headscale-admin , a web UI for users, pre-auth keys, and nodes. Run it next to Headscale and serve it from the same domain under /admin:
docker run -d --name headscale-admin \
  -p 8000:80 \
  goodieshq/headscale-admin:latest
# reverse-proxy https://headscale.example.com/admin → localhost:8000
The panel authenticates against Headscale with an API key, so mint one:
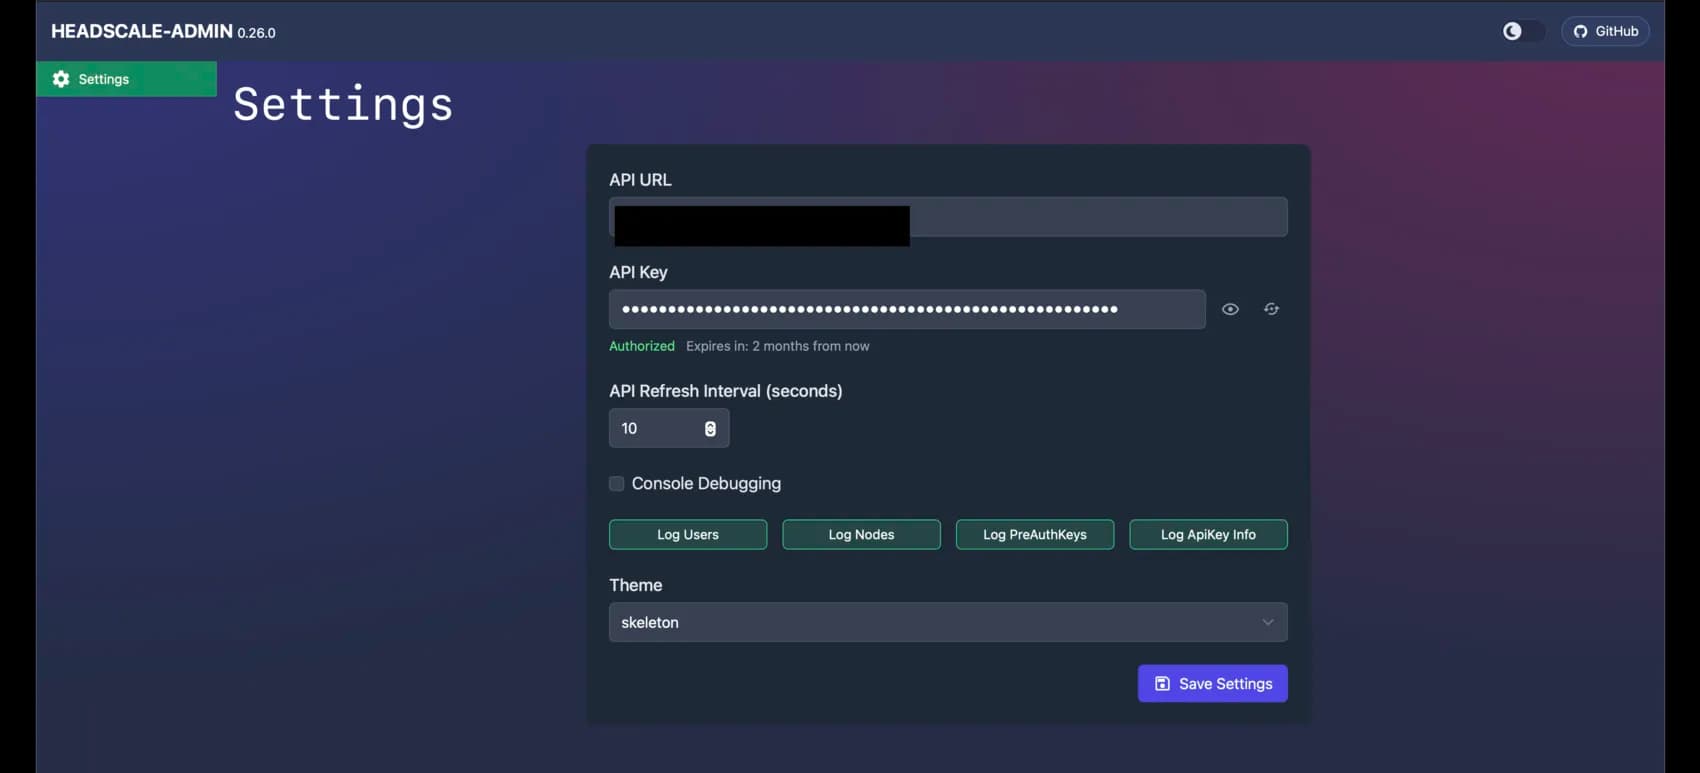
docker exec headscale headscale apikeys create --expiration 90dOpen https://headscale.example.com/admin → Settings, set the API URL to your control server, paste the API key, and save. Once it reads Authorized, you're connected. This is the last time you touch the terminal.
Create a user
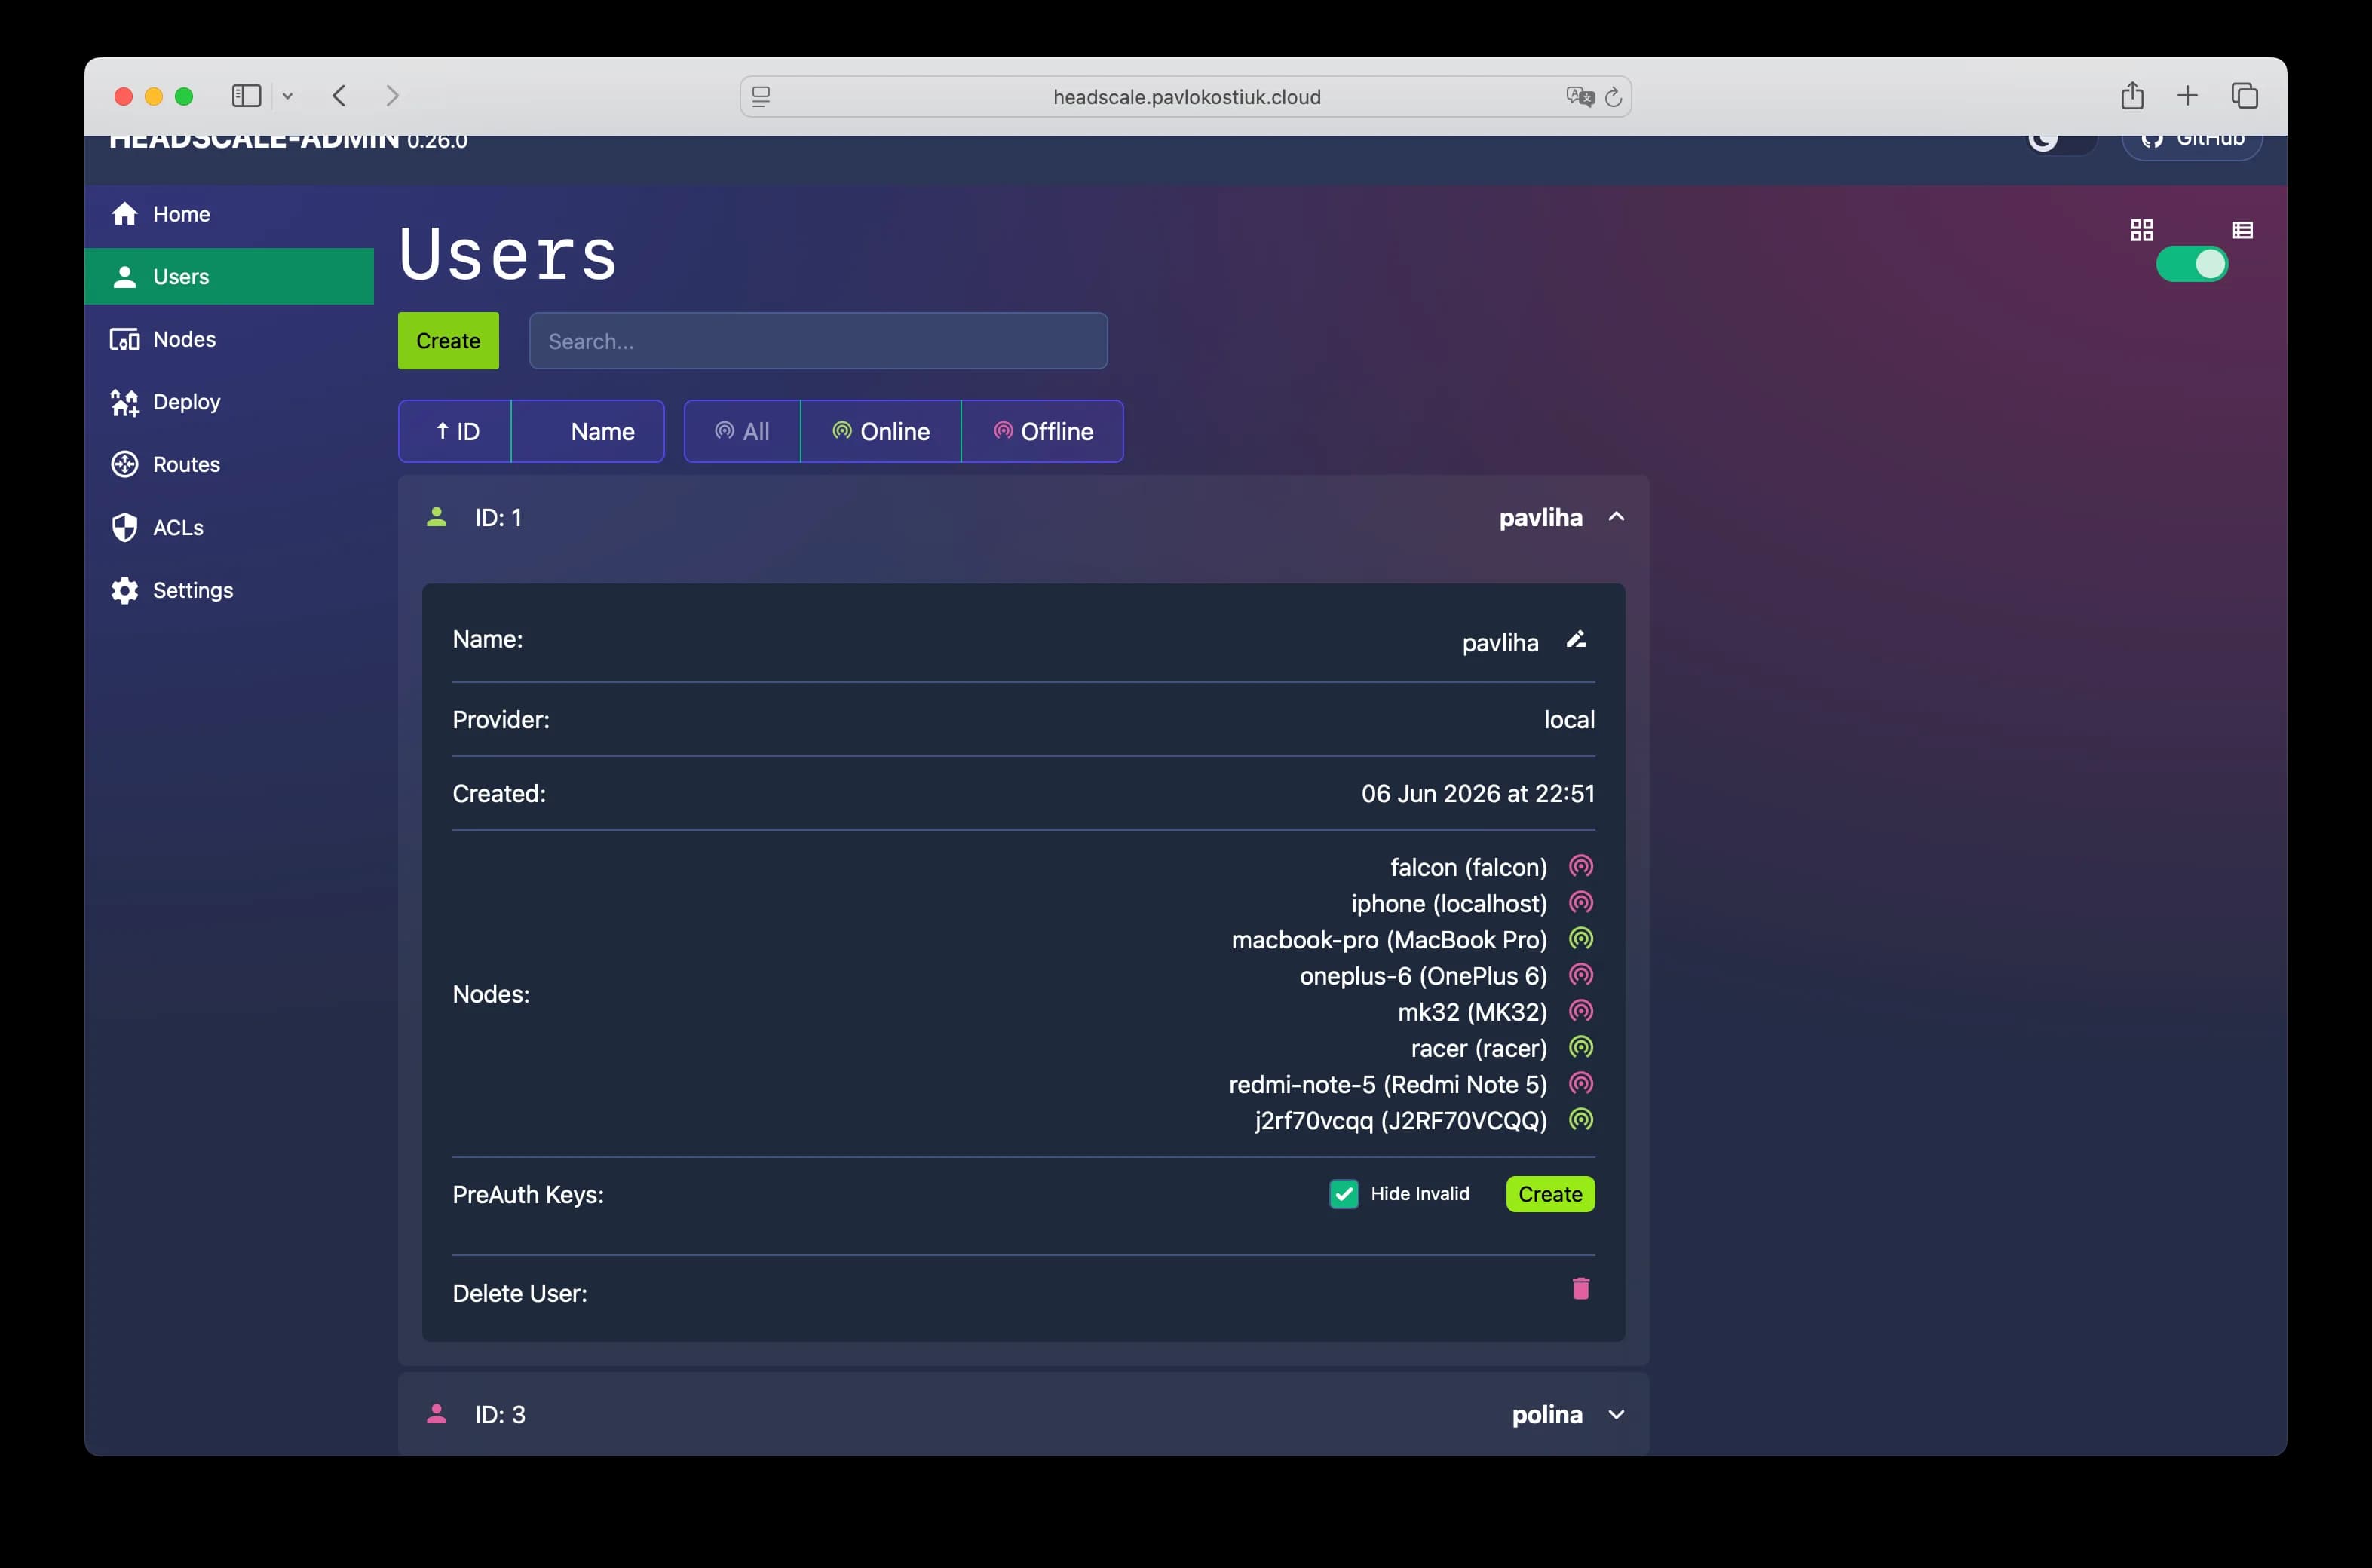
Devices register under a user (a namespace). In the Users tab, click Create and name it. The user's card then lists every node it owns and its pre-auth keys:
Mint a pre-auth key
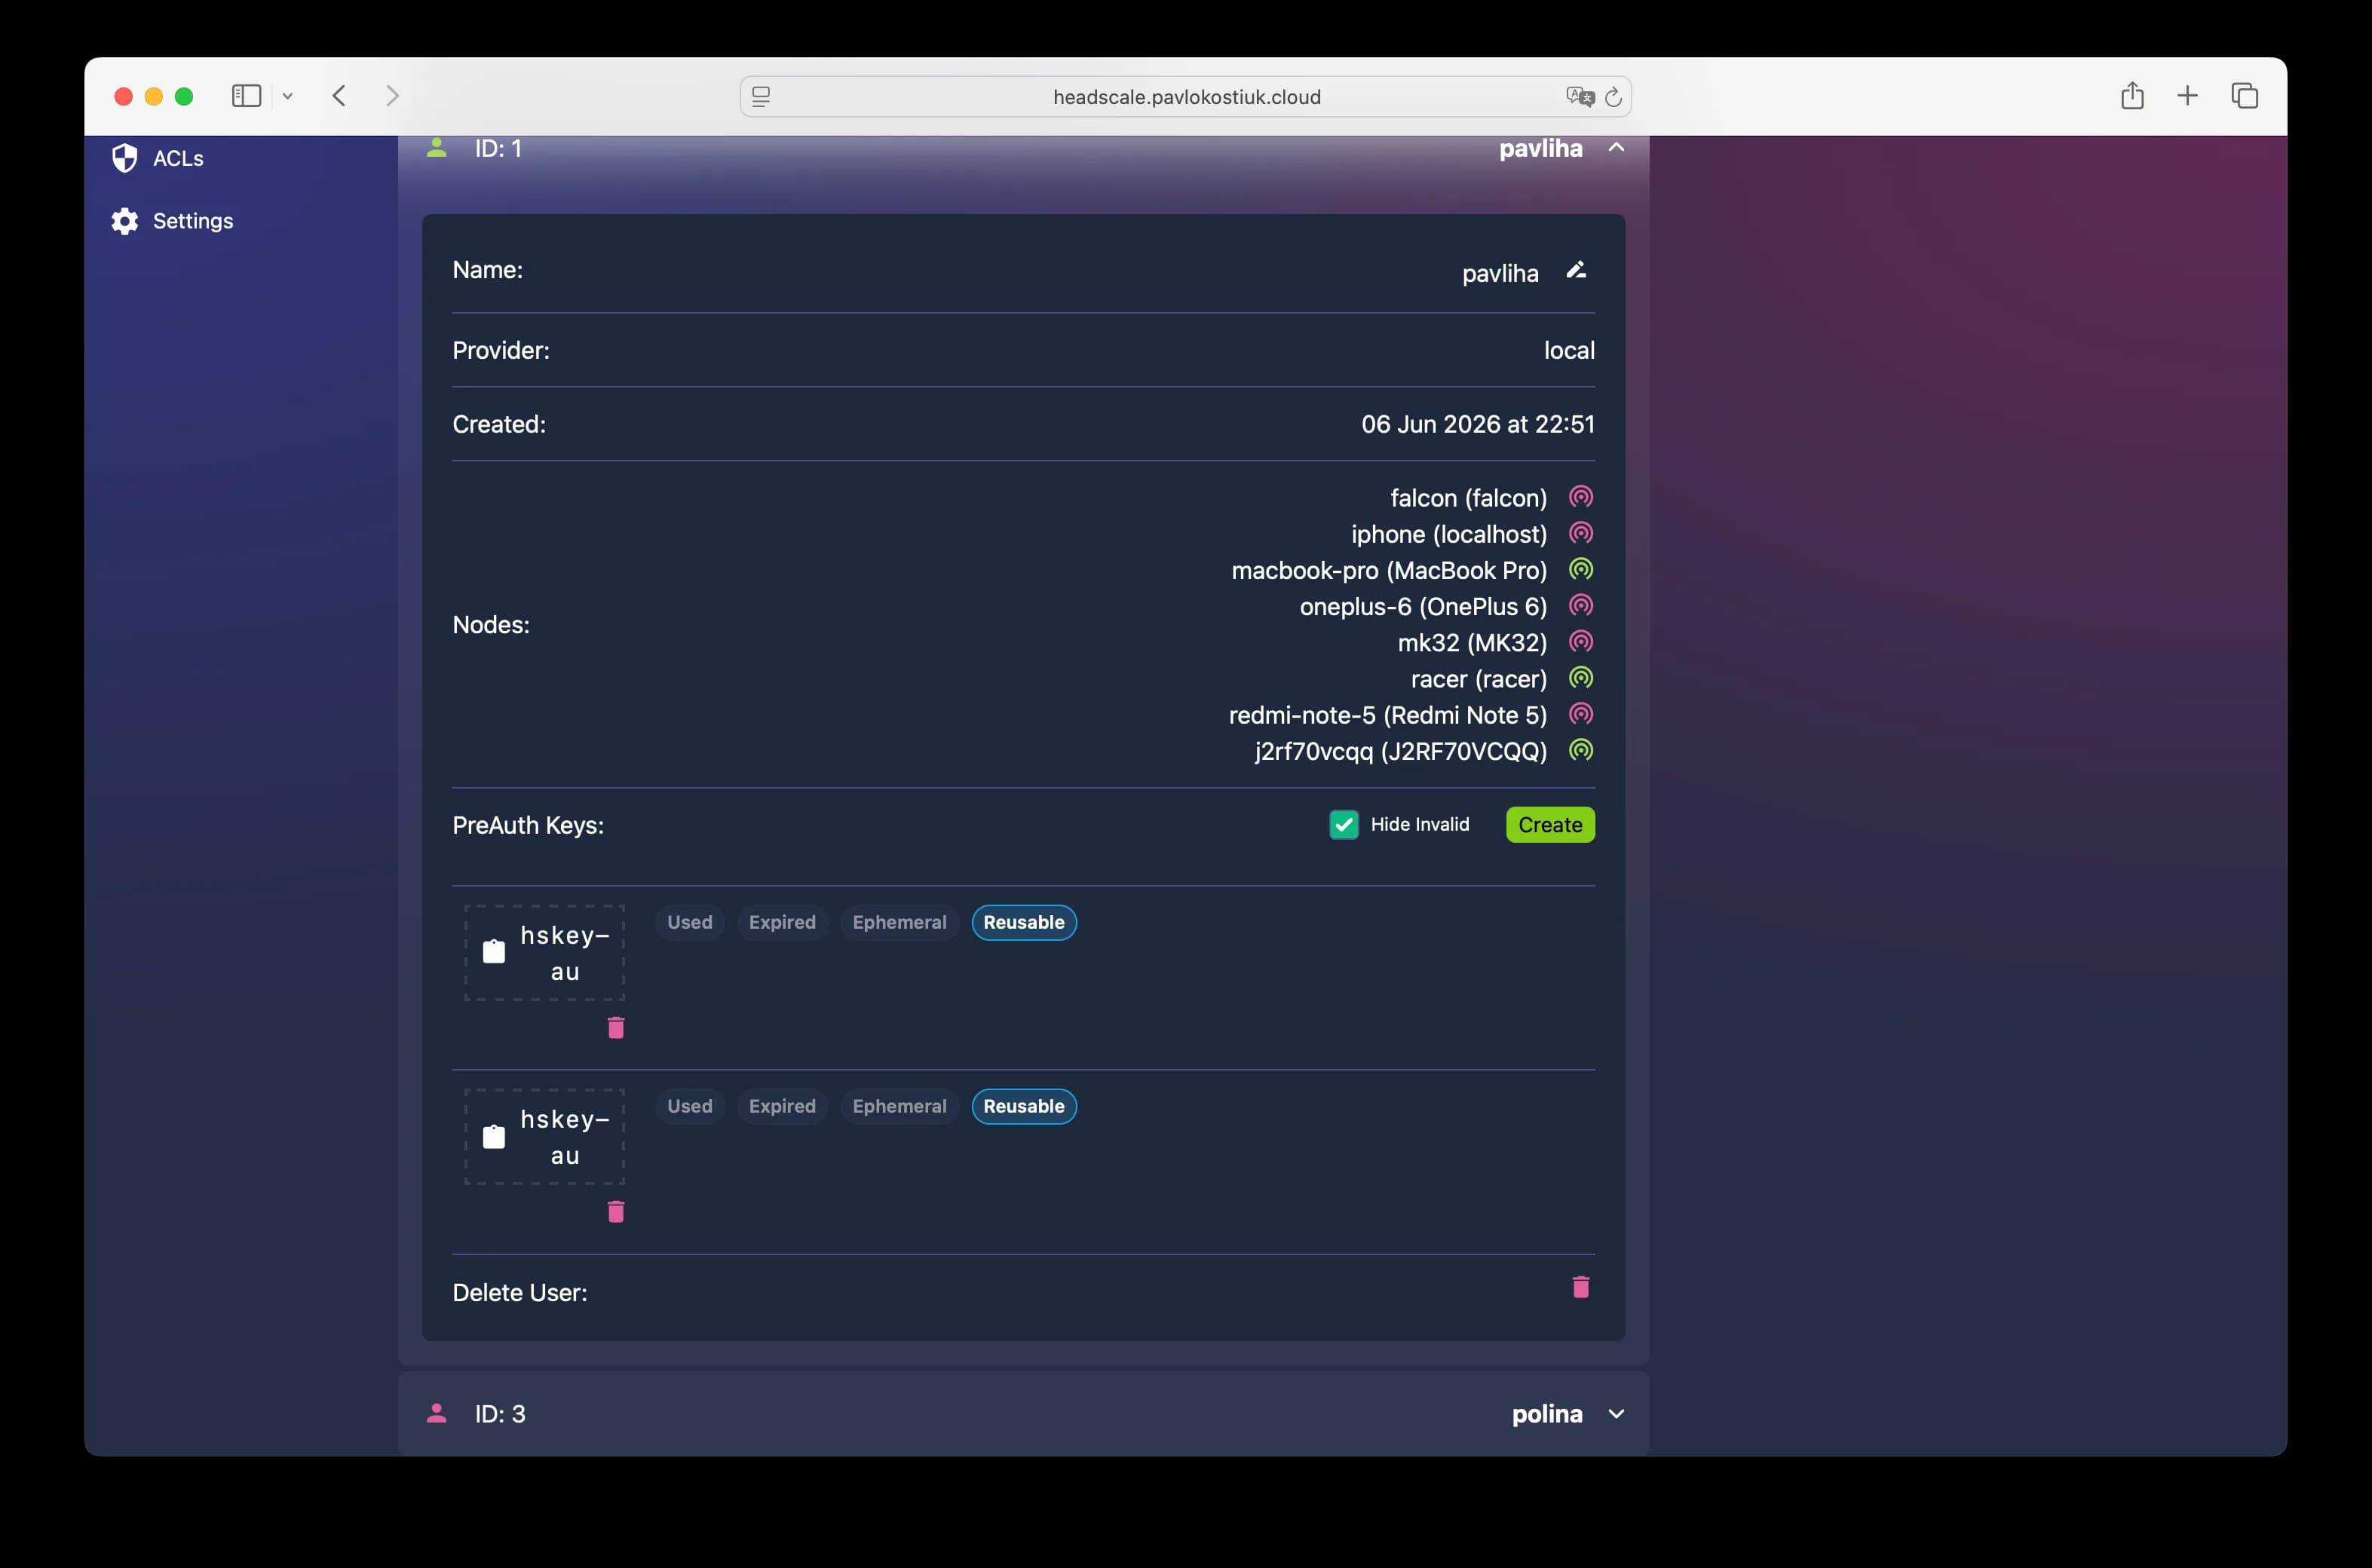
A pre-auth key lets the device join unattended, with no browser sign-in and no manual approval. This is the path Aircast is built around. On the user's card, next to PreAuth Keys, click Create. Copy the hskey-… value, which you'll paste into the device in the next step.
Point the device at your server
Open the device on your LAN (http://<hostname>.local), go to Settings → Device → Connection, and find the Tailscale card. Expand Control server and enter:
- Control server URL: your URL, e.g.
https://headscale.example.com - Auth key: the pre-auth key from step 4
Press Save, then Connect to headscale.example.com (or Switch to headscale.example.com, if the device is already on another tailnet). The device registers itself against your Headscale and appears under the key's user within a few seconds, with no approval step.
Flashing a new card? In the Flasher's Remote access section, pick Headscale, enter the Control server URL, and paste the pre-auth key (or a Headscale API key, then pick the user). The drone joins your tailnet on first boot.
Confirm it joined
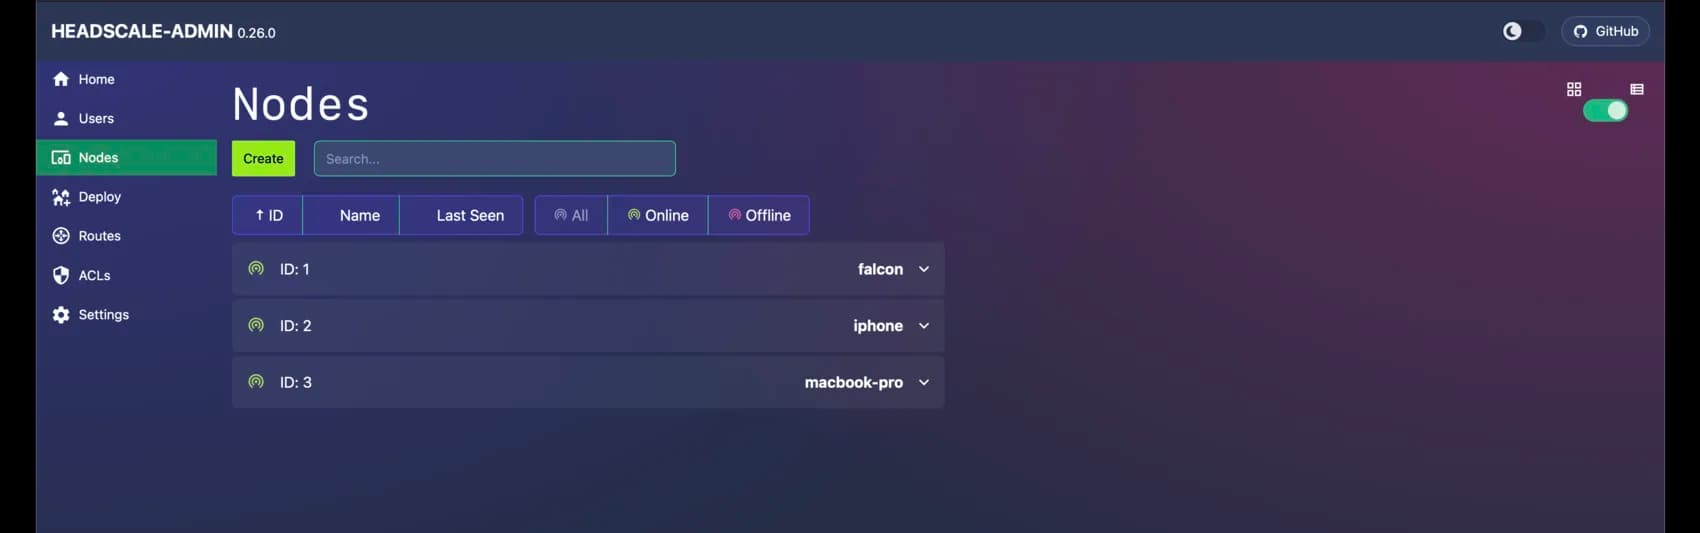
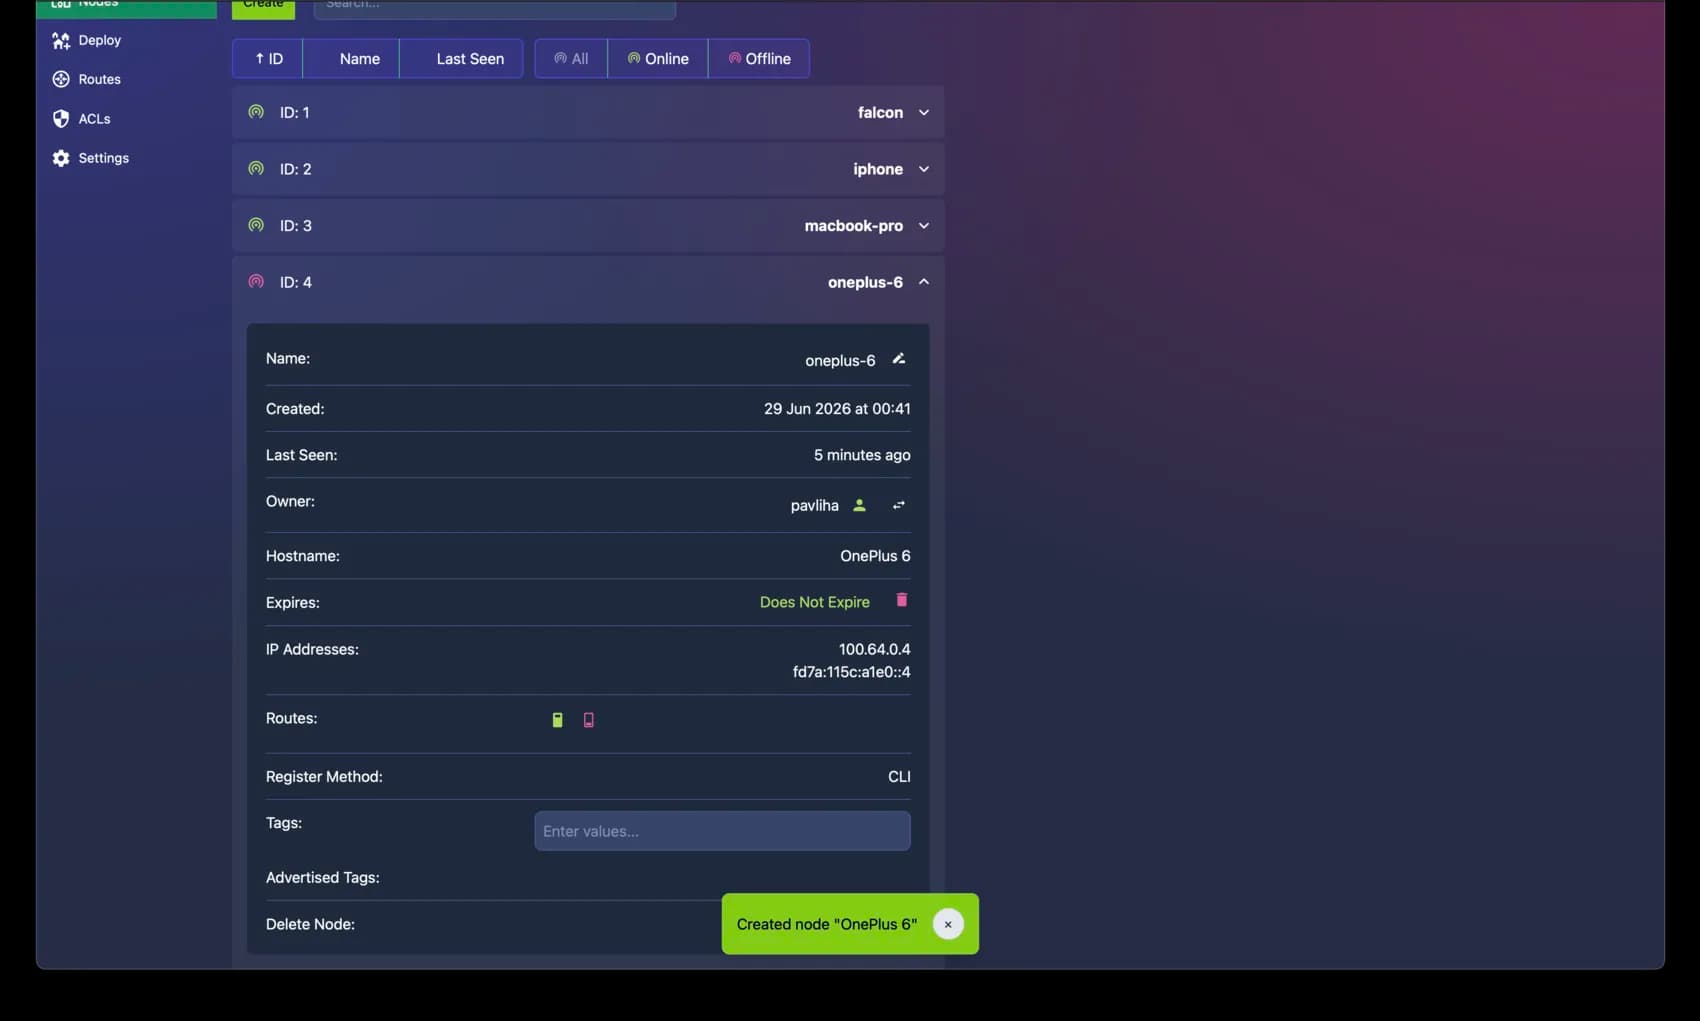
The admin panel's Nodes tab lists every registered device with its online status and tailnet IP. Your Aircast device shows up here alongside any phones or laptops on the tailnet. The device's Tailscale card now reads connected with its tailnet name, and you can reach it at that address from anywhere on the same tailnet.
Join your viewing devices
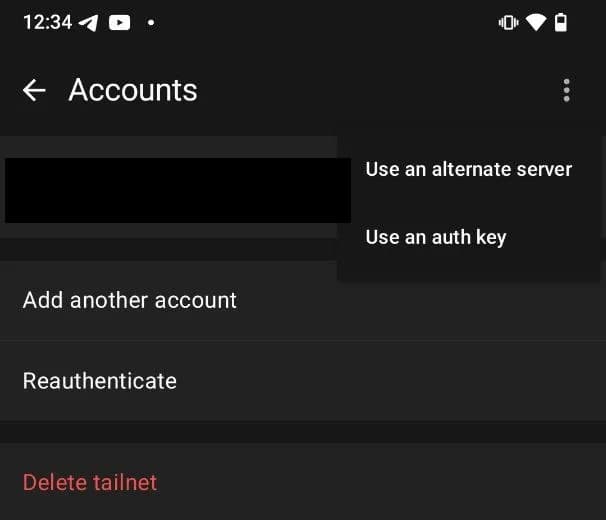
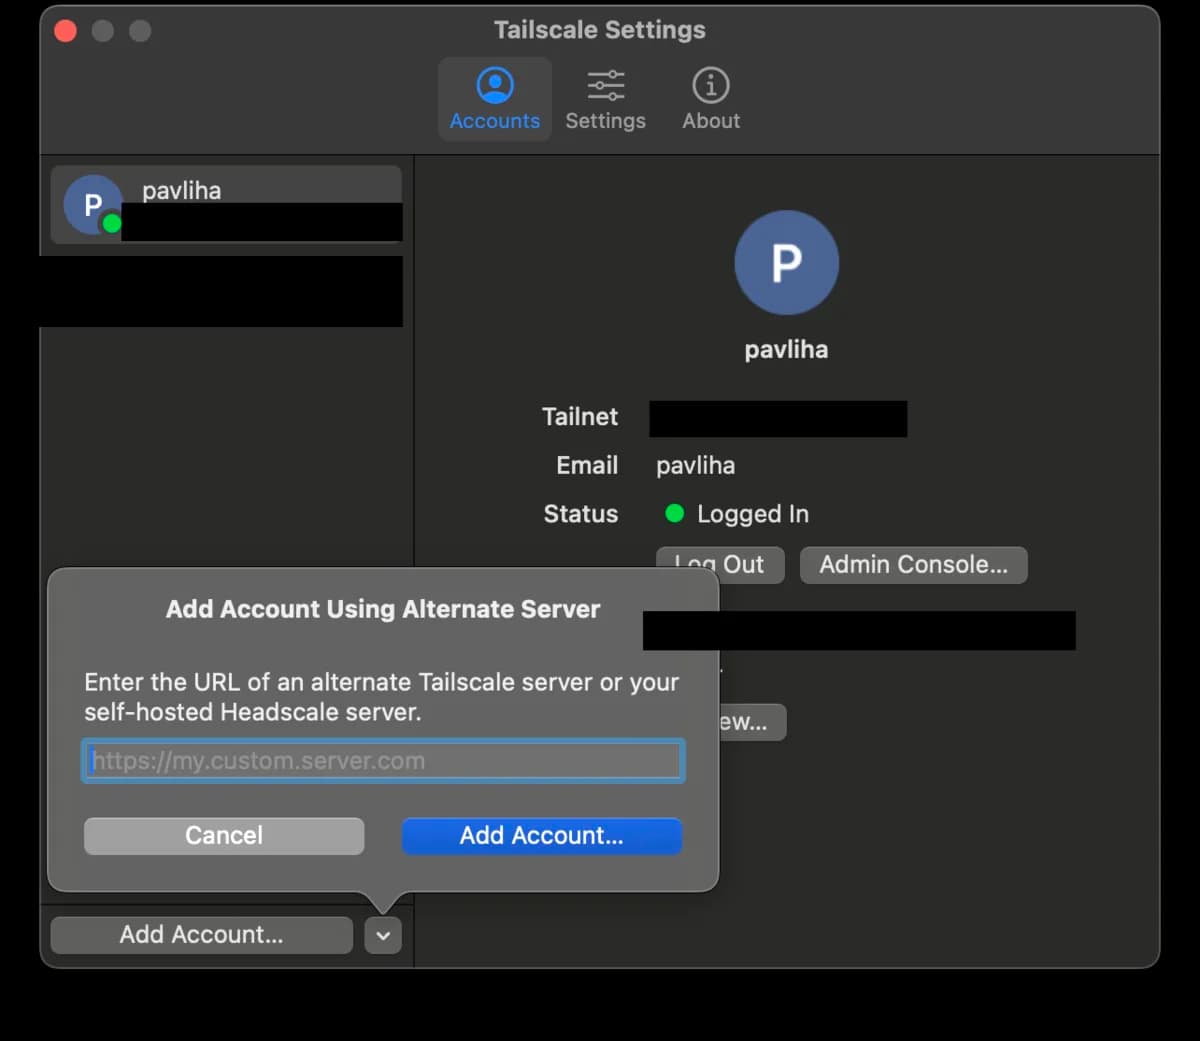
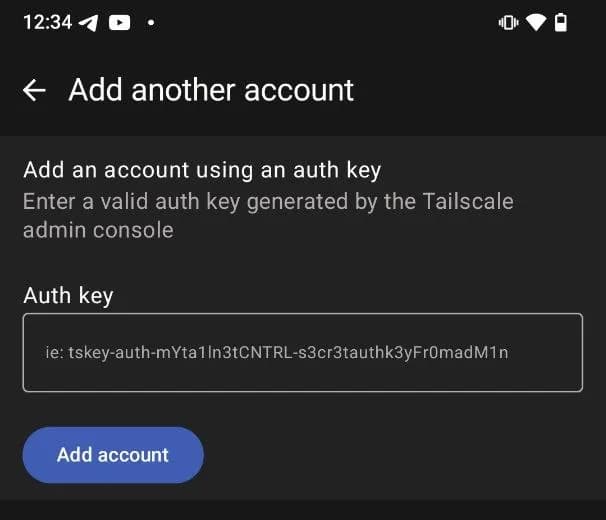
To watch the stream, the device you view from, a phone or laptop, also needs to be on your tailnet. In the official Tailscale app, add an account with Use an alternate server and enter your Headscale URL, and the app signs in against your control plane instead of Tailscale's.
On a phone, open the account menu and pick Use an alternate server:
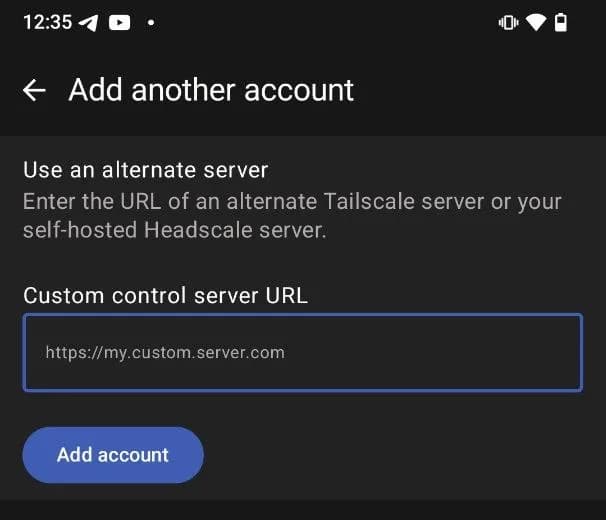
On macOS or desktop it's the same: Add Account → Use an alternate server, then enter your Headscale URL:
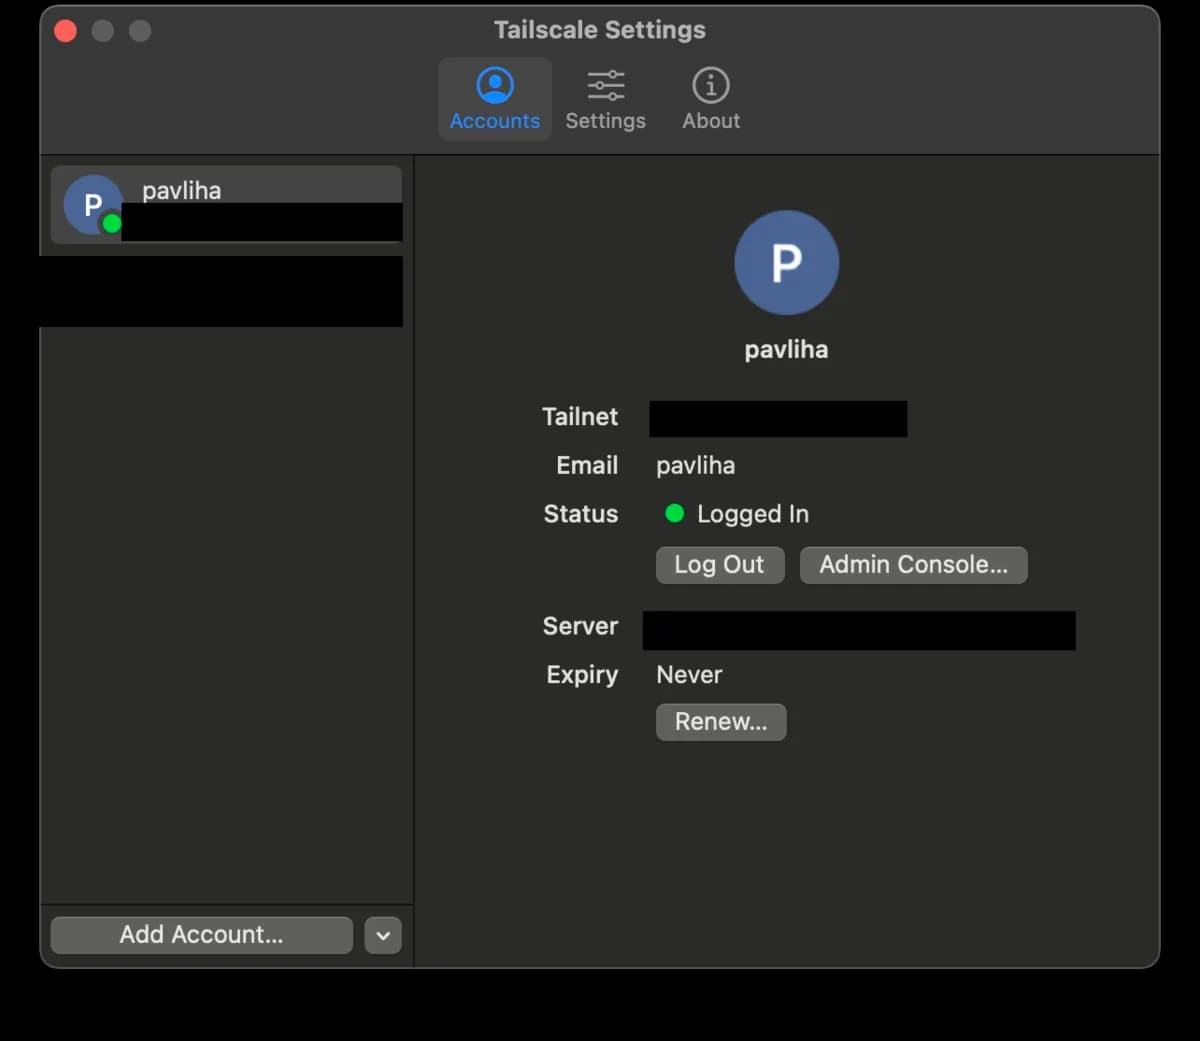
Once it connects, the account's Server shows your Headscale URL, confirming the device is on your control plane, not Tailscale's:
Joining unattended (CLI, or a machine without a browser)? tailscale up --login-server https://headscale.example.com --authkey <pre-auth key>, the app's Use an auth key option does the same.
Connect QGroundControl over the tailnet
With both ends on the tailnet, your ground station reaches the device by its tailnet address, with no port forwarding, no public exposure. In Aircast QGC, point telemetry at the device's tailnet IP or name, and video follows.
Telemetry (MAVLink)
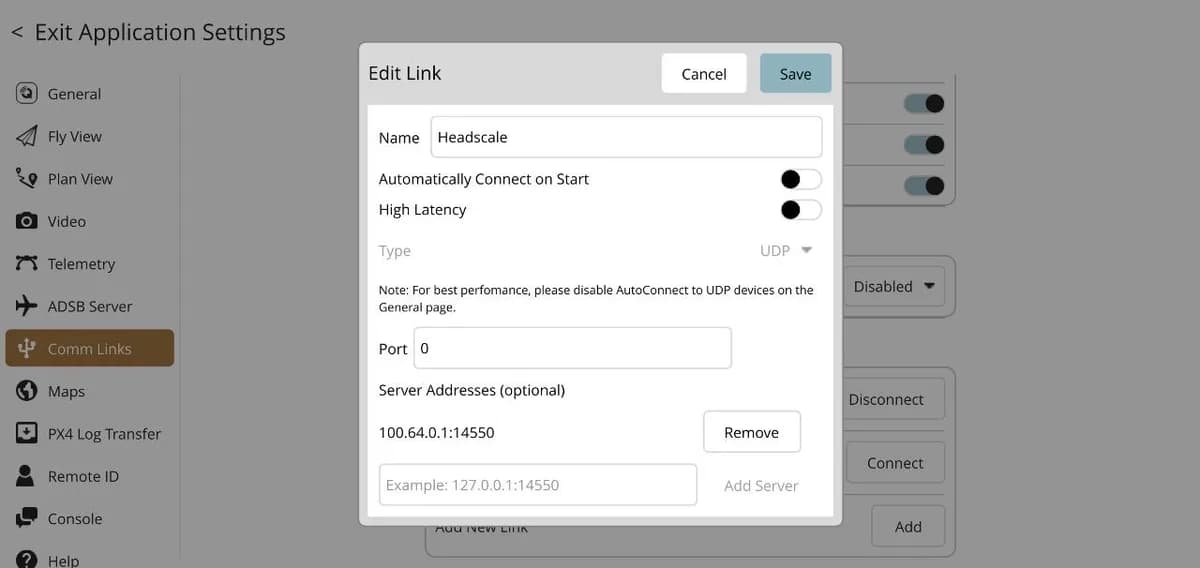
Open Application Settings → Comm Links → Add. Create a UDP link and add a server address pointing at the device's tailnet IP on the MAVLink port, typically <device-tailnet-ip>:14550:
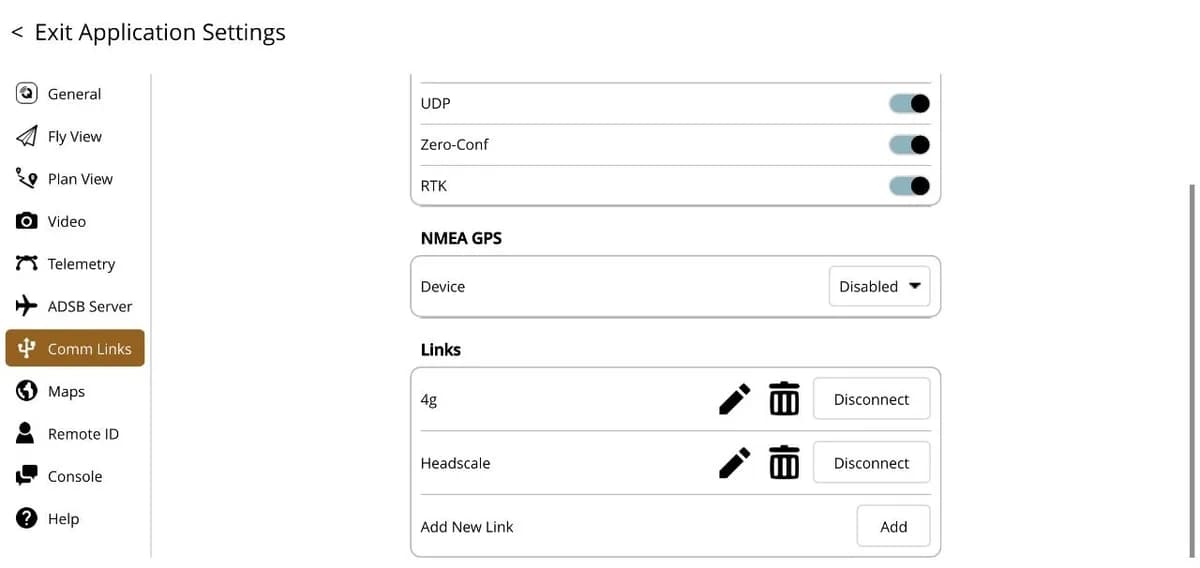
Save it, then Connect: it sits alongside any other links (e.g. a direct 4G link) so you can switch between paths:
Video (RTSP)
Once telemetry arrives over this link, the device announces its camera and Aircast QGC sets up Camera 1 by itself. For another camera, or a ground station that doesn't pick it up, open Application Settings → Video, press Add camera stream under Cameras, and use the device's tailnet name: rtsp://<device-tailnet-host>:8554/<camera name>.
Troubleshooting: “key hex string doesn't have expected type prefix mkey:”
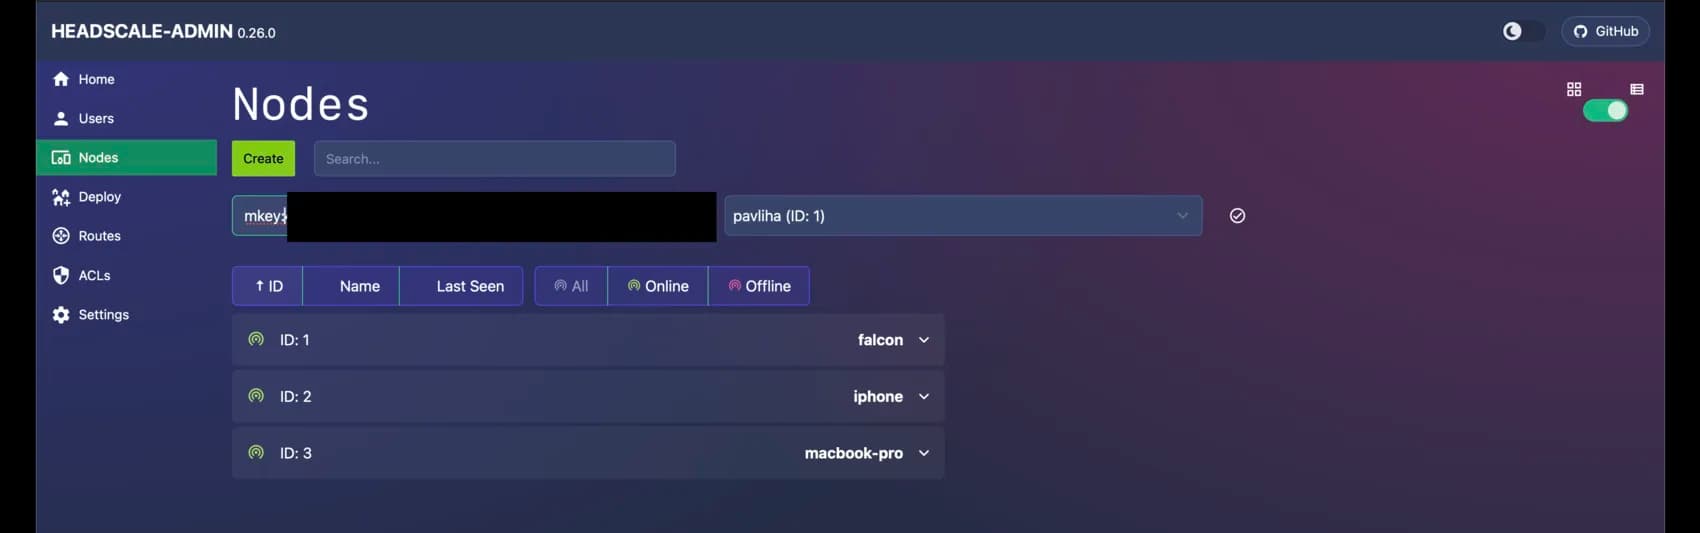
mkey: to copy, no Create form and no approval. Use the manual flow below only if you specifically want to approve each node by hand.If you do register a node through headscale-admin's Create form, you'll hit this error when you paste a key without its mkey: prefix. The field wants the full prefixed key, not the bare hex.
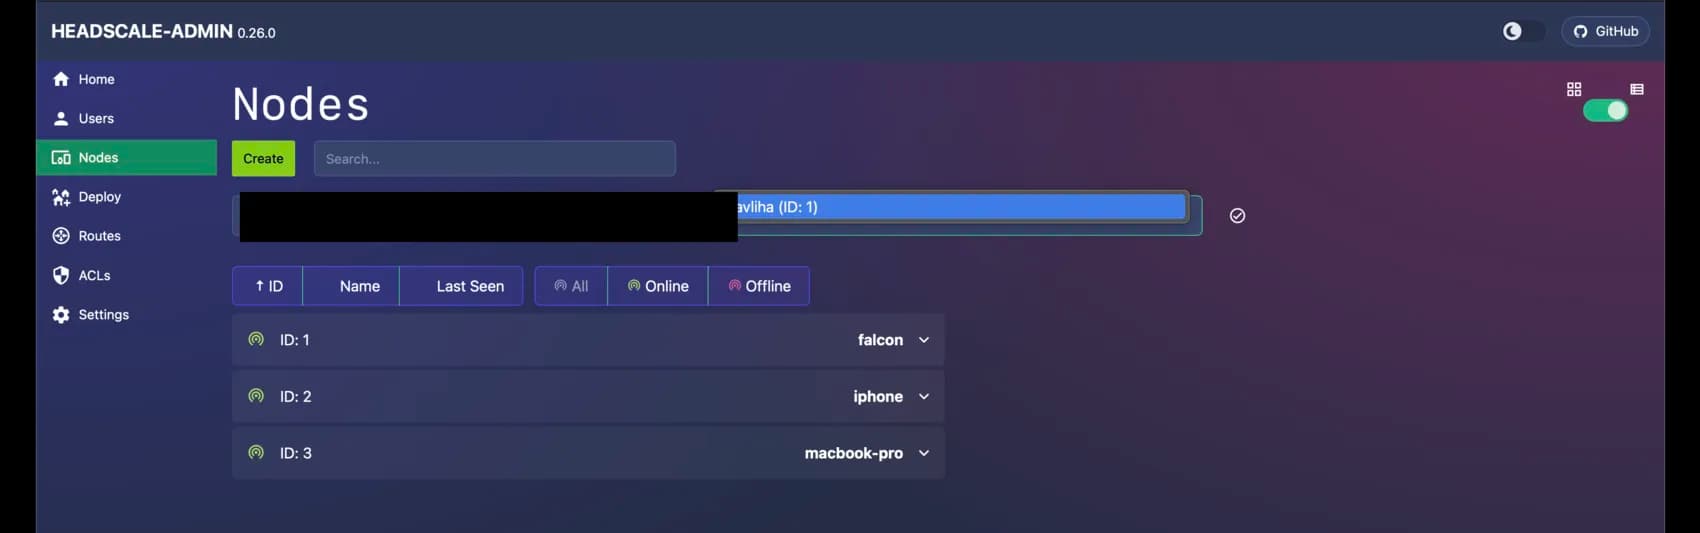
Where does the key come from? A node can't be created from a hostname. It only exists once the device starts registration, which is what generates its machine key. When a client signs in to a self-hosted Headscale interactively, it shows a Machine registration page with a ready-to-run command. The value after --key, including the mkey: prefix, is exactly what the form expects.
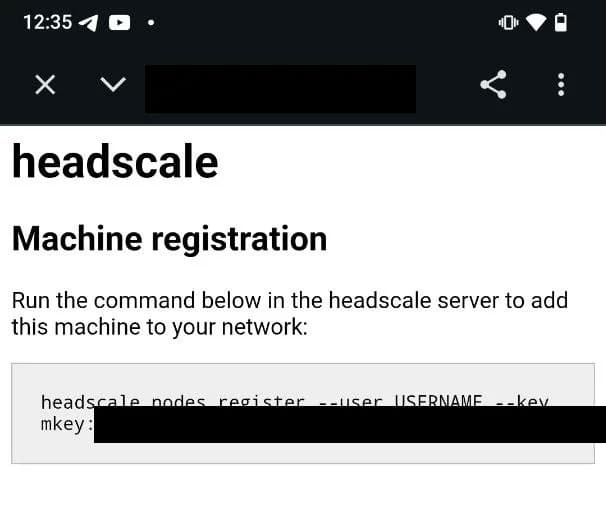
Paste that full mkey:-prefixed value into the Create form, pick the user, and submit. The node registers cleanly.
Flash your card in about 5 minutes
The Aircast Flasher downloads the image, sets Wi-Fi and hostname, and verifies the card.
On This Page